A deployment spread across dozens of sites: more than fifty solar installations, a dozen or so wind sites, and around ten hydro sites. The network at each one looks about the same: a router with a 4G SIM, an unmanaged switch, an NVR with seven to fifteen cameras, plus an alarm panel and a few pairs of fiber media converters. The problem that comes up most often is a SIM card running out of data before the month ends. The bill shows how much a site used, never which device used it. On the requirements list, one line stands out: network analysis that works out of the box.
When a dozen or so devices sit behind one industrial cellular router, working out which one is using the data takes four layers. Every device needs an identity first. Traffic has to be separable by that identity. The unit at the edge of the network has to meter it. Only after metering can a single device be singled out. Drop any one layer and the rest comes down to guesswork.
With enough sites, addresses are handed out automatically, and which device is which depends on a spreadsheet nobody has updated in a long while. The first thing to add is not a rule but a list. Two things are worth checking: which endpoints are connected right now and where each one is talking to, and whether the mapping between addresses and MAC addresses has been pinned down. Once that is done, it becomes possible to say, device by device, where each one is installed and what it may reach. What cannot be accounted for is what deserves investigating. A MAC address in the lease table that appears on no inventory is usually a commissioning laptop left plugged in or a device added later, and those tend to keep sending data.
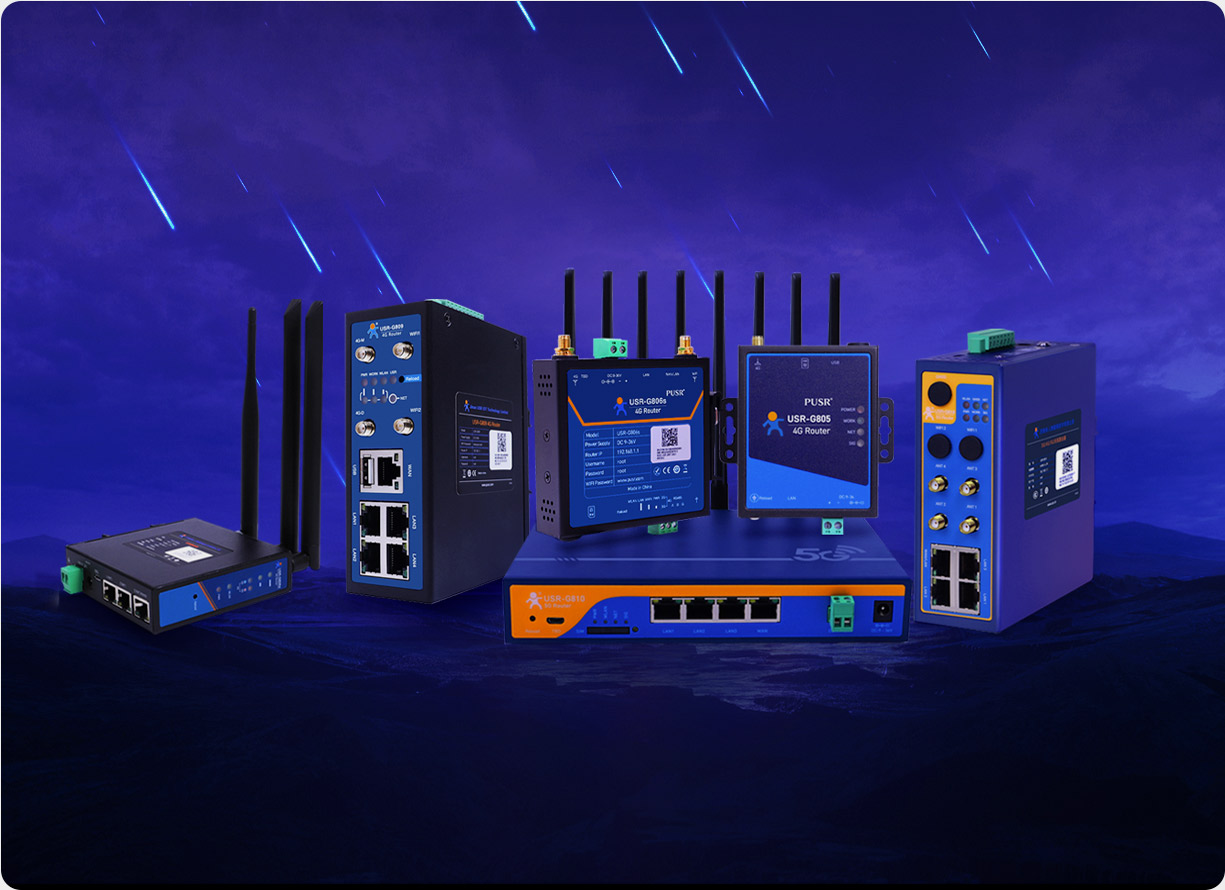
The requirements this places on the hardware are specific: live sessions have to be visible, assigned leases have to be readable with hostname, MAC address and IP address in one place, and both have to be lockable. The USR-G806w datasheet covers all three. Live sessions give one view of the connections each endpoint holds, which is how an odd one gets spotted quickly. On the LAN side it supports VLAN assignment and static MAC-to-IP binding. It also exposes an API for basic device information, so connecting an internal system does not mean buying a centralized network management platform.
Splitting by device type is less useful than splitting by what each device sends out. Video runs continuously, and one camera plus whatever the NVR syncs in the background is usually the largest single item on a site. Acquisition traffic from PLCs and data loggers arrives as a few dozen to a few hundred bytes every few minutes, small in volume but sensitive to queue position. Human endpoints, inspection laptops and commissioning tools, move little data but do it in concentrated bursts.
Once the groups are defined, totals per segment narrow the search from a dozen devices to three or four. The USR-G809s contributes port count at this layer: two ports configurable as WAN or LAN, six LAN ports, and two SFP slots, so with one segment per port every gateway stays on the same box and no extra switch is needed. It mounts on a DIN rail, runs on DC 9-60 V with reverse polarity protection, and fits wherever a gap in the cabinet allows.
Metering has to happen on the router itself, not after a platform sends the numbers back. One line on that list settles the matter: no centralized network management software is going to be bought. Trends, thresholds and alerts therefore have to be visible on the device and configurable there. Two things matter: the trend, with daily and monthly usage side by side so the monthly average can be projected, and the moment, meaning which day and which part of the day the usage jumped. The threshold belongs at 70 to 80 percent of the plan allowance, with the alert going out by email or SMS rather than arriving with the bill. Where one unit carries two kinds of traffic, policy routing can send each one out through its own interface, public and private networks kept apart, so which SIM the usage lands on is clear from the start.
The USR-G816 handles this leg. It supports both 5G SA and NSA, with more uplink than 4G, which means filling a plan faster as well as working faster. Traffic overrun is one of its three alert types, alongside offline and weak signal, and all three go out by email or SMS with repeated push supported. Through the remote management platform, parameters, reboots and firmware upgrades can all be handled remotely. RS232 and RS485 terminals are on board as well, so a data logger connects directly and no separate serial server is needed. Two SIM slots are provided, the second optionally an embedded eSIM, which means changing plan or carrier involves no hardware change. The metal housing is built for wide voltage and wide temperature, rated from -35 to 75 degrees Celsius.
After the first three layers, the search has come down from a whole site to three or four devices in one segment. The last step needs no elaborate tooling, just comparison. Set a deliberately generous cap, apply it by address range or by MAC, and run for two days to see whether the curve moves. If nothing changes, disconnect devices one at a time; the one whose removal drops the curve is the one. A reading before and after each disconnection gives a difference that counts as evidence, more reliable than an impression. No laptop needs to travel to the site either, since ping, traceroute, nslookup and packet capture are built into the device, along with a one-click system diagnostic.
There is an order to the checks. Video comes first, since background cloud sync is the most common single item. Bulk firmware upgrades and historical playback belong in a night window. Where a site can get fixed broadband, the wired link becomes primary and cellular falls back to backup, with the switchover handled by the device itself.
With two or three devices at a location, the identity list plus metering is enough and segmentation can be skipped. Past ten devices with video in the mix, all four layers are needed. Once sites multiply, the economical approach is not tuning each one but templating the rules: moving a segment rule to another site means changing only the destination address and port, exporting configurations with the site number and date in the filename, and verifying once at the busiest hour.
What is worth asking when choosing hardware is not the headline throughput but whether the following are actually possible: seeing which endpoints are connected right now, counting usage separately per segment, alerting before the bill arrives, and applying a rule to a single device. With all four available, the number of devices behind one industrial cellular router stops being a matter of guesswork.
Three things differ: environment, interfaces, and remote maintenance. On environment, the metal housing, wide voltage and wide temperature range, and DIN rail or wall mounting put the USR-G806w at -20 to 70 degrees Celsius and the USR-G816 at -35 to 75 degrees Celsius, both with hardware and software watchdogs that recover the unit on their own. Consumer hardware is designed for room temperature, so in a cabinet it is the first thing to give out in summer. On interfaces, the USR-G816 also carries RS232 and RS485 terminals, so older PLCs and data loggers connect directly and one serial server stays out of the cabinet. On remote maintenance, alerts are pushed out and both parameters and firmware can be changed from elsewhere, so a site does not need a visit every time.
Port count and client capacity matter, but the more useful question is where each type of traffic goes. The USR-G809s leaves room in ports: two configurable as WAN or LAN, six LAN, and two SFP, so with one segment per port every gateway sits on the same box and the cabinet needs no second switch. Running out of ports and hanging a switch underneath costs visibility, because traffic is then only visible down to the switch, not to the individual device. On camera-heavy sites, a model with enough ports is the safer choice.
The answer depends on uplink. Acquisition traffic, a few dozen to a few hundred bytes at a time, is fine on 4G. Uploading video, or running several video streams and remote playback at one site, hits the uplink ceiling first, and that is when 5G earns its place. The USR-G816 uses a Qualcomm X62 modem and supports both SA and NSA, with more uplink than 4G. Wider uplink also means the plan runs out faster, so traffic alerts and thresholds have to be configured together with it. Sites without 5G coverage stay on 4G, and the frequency bands in use locally are worth checking before ordering.
Switchover is triggered by link availability, not by signal bars. The USR-G816 lists WAN failover, meaning the unit moves to the backup network automatically when the primary becomes unusable, with cellular, wired and Wi-Fi able to back each other up. A weak signal on its own does not necessarily trigger the switch, which is why weak signal is its own alert category, sent by email or SMS alongside offline and traffic overrun, with repeated push supported. Detection method, decision delay and whether thresholds are configurable vary by model, so confirming against the specific datasheet is the safer route.
It comes down to bitrate: bitrate in Mbps multiplied by seconds, divided by 8, divided by 1024, gives gigabytes. A 1080p camera on H.265 with a 2 Mbps mainstream runs to roughly 21 GB per day if it uploads continuously, which is around 600 GB in a month. H.264 needs a higher bitrate, so the figure climbs from there. This is why cameras in the field usually record to a local NVR and only send alarm clips and snapshots out, with remote playback as an occasional action. Once continuous cloud sync is switched on in the background, usage follows the curve above and the plan empties quickly.
Three things: watch the daily and monthly usage trend, configure the traffic overrun alert, and put a cap on the address ranges that matter. The first two are on both the USR-G806w and the USR-G816, with alerts by email or SMS and repeated push supported. The threshold belongs at 70 to 80 percent of the allowance, leaving time to act. The third means rate limiting by address range or by MAC, starting with a generous cap, running two days, checking whether the curve moves, then tightening. Where one unit carries two kinds of traffic, policy routing sends each out through its own interface, so which SIM the usage lands on is clear from the start.
The public internet carries traffic unencrypted, so tunnels and separation have to make up for it. Encryption comes from VPN: these PUSR models support OpenVPN, IPsec, PPTP, L2TP and GRE, with the OpenVPN implementation extended to connect to three servers at once or act as a server itself, and .ovpn files along with PKCS#12 certificates import in one step instead of parameter by parameter. Separation comes from VLANs and firewall rules, with cameras, controllers and inspection terminals each on their own segment. Three basics go with it: change the default password, keep firmware current, and give remote access accounts separate levels. Several PUSR devices have been certified to EN 18031, the EU cyber security standard under the RED directive, and the certificate scope is worth asking for when selecting a model.
It does not. The PUSR Remote Management platform reaches the built-in web interface of each device from elsewhere, and parameters, reboots and firmware upgrades can all be handled through it; with many sites, templating the configuration beats adjusting each unit. The absence of a fixed public IP at the site does not block remote access either, because the VPN tunnel is initiated outwar