On a packaging line, the PLC sits on the left side of the cabinet, the HMI on the front panel, the code reader at the discharge end, the supervisor PC in the next room, and two cameras were added at the critical stations. When the quotation reaches the line item for networked devices, the question turns concrete: an industrial wireless router carries only three or four Ethernet ports, and the remaining devices have nowhere to plug in.
A cheaper route has been tried elsewhere. A phone hotspot overheats once several terminals connect, so the phone is tethered by cable to a portable router, and the portable router broadcasts the Wi-Fi. What makes that arrangement worth noting is the split of duties: the phone handles egress, the portable router handles distribution. The shop floor draws the same line.
Whether a second unit is needed starts with counting ports. The egress unit has to keep at least one port for the uplink, and whatever remains is the number of access ports available to field devices. Copy the list off the floor: one for the PLC, one for the HMI, one for the supervisor PC, one per camera, one each for the code reader and the handheld terminal. Once that total exceeds the remaining access ports, the second unit stops being optional. It is also worth holding one port back for commissioning, when a laptop has to go on the line without unplugging a camera.
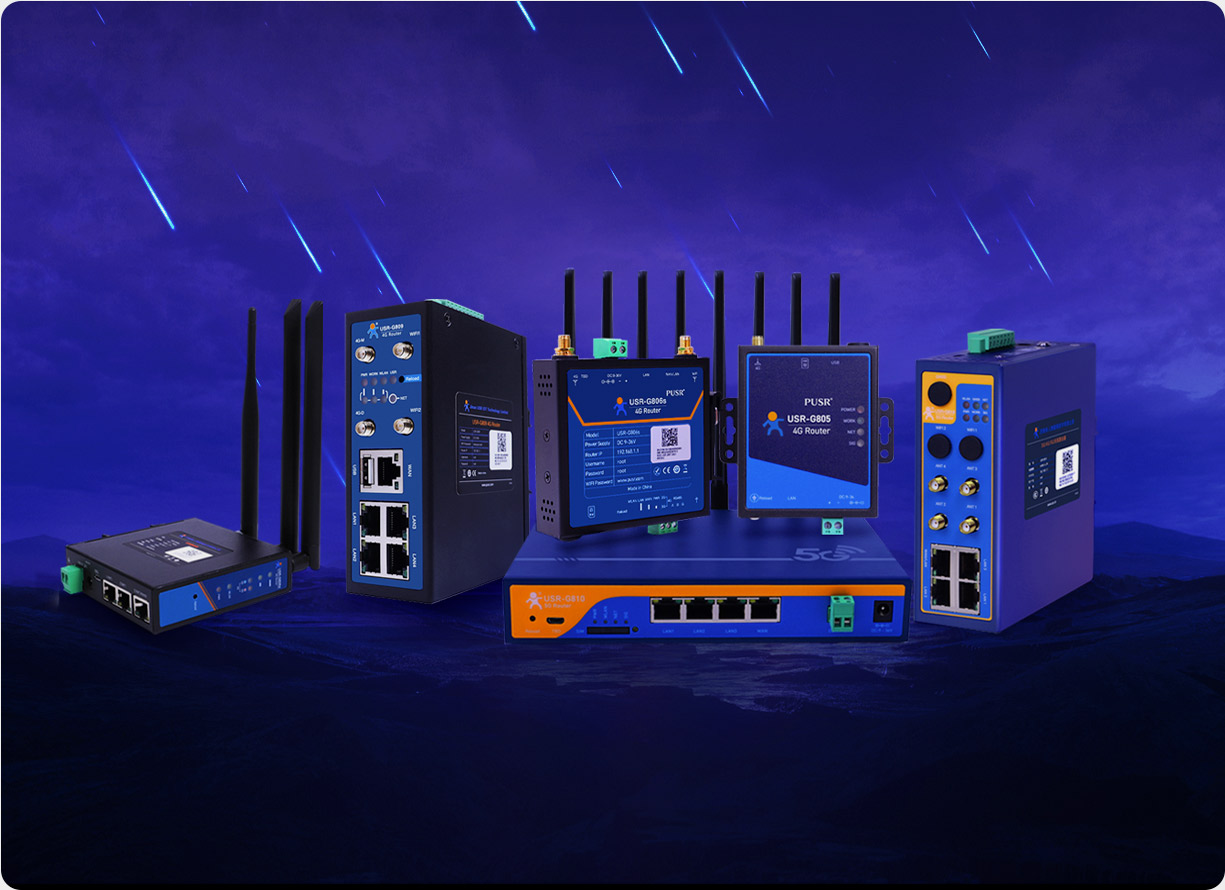
The estimate usually goes wrong because the list is drawn from today's device count. One line change, one added workstation, and the ports run out. USR-G809s fits this kind of site: two gigabit ports configurable as WAN or LAN, six LAN ports, plus two SFP fiber ports, one of which shares its slot with a copper port. A station with around ten devices normally does not need a switch hung beneath it, and one device fewer means one power feed, one cable run and one acceptance test fewer.
Not every port shortage is solved by adding a unit. The first question is which of these devices must see each other, and which must not. Where the camera segment and the supervisor segment are meant to stay apart, the unit being added is not one that only forwards frames: the model has to support VLAN segmentation, and three places have to be configured together, the router side, the switch side and the wireless access point. Leave one out and the separation exists only on paper.
Adding the second unit puts one more link segment in the cabinet, and the cost concentrates there: devices beneath it reach the internet through that single LAN port on the router. Traffic between devices on site never touches the uplink, since recordings stay on the local recorder and collected data lands locally first, so daily uplink barely moves. What consumes the allowance is remote viewing, cloud backup and bulk firmware upgrades. The way to size it is to log uplink during the busiest hours, once in the morning, once around noon, once in the evening, and take the value that holds rather than the peak. Camera traffic has its own arithmetic: bitrate in Mbps times seconds, divided by 8, divided again by 1024, gives GB. A 1080p stream at 2 Mbps running upstream without pause works out to roughly 21 GB a day, about 600 GB a month, which is why recordings usually stay on a local recorder and only alarm clips leave the site.
The forwarding-only unit takes no part in address assignment or access control; DHCP, the gateway and the firewall rules stay on the egress unit. That leads to something routinely missed: the rule count grows with the device count. Allowed rules are added one by one with a catch-all deny pressed at the end, so twenty devices mean twenty-odd rules. Source MAC and source IP are mutually exclusive inside a single rule, which means one field is left blank. The target zone deserves the same care: where firmware splits it into wired and cellular zones, ticking only the link in use leaves the rule blind the moment failover switches. Where the aim is a domain rather than a fixed address, the access restriction list takes over, and selecting whitelist mode without adding a single entry blocks every domain. Changes take effect only after a restart from the system menu. Acceptance then comes free: machines on the list cannot reach the internet and can still ping each other, and that test run is itself the handover record.
The last layer is the one most often skipped: one more device is one more failure point, and its failure surface is wider than that of the egress unit, because a power loss takes down everything hanging beneath it. Model selection looks at the same few items: a wide-voltage terminal block fed from cabinet DC (24 V dips the instant motors start and stop), reverse polarity protection, a metal case for heat conduction, DIN rail mounting, wide operating temperature. USR-G816 and USR-G806w are both built to those lines. The former, a 5G model on a Qualcomm X62 module, has a metal case rated -35 to 75 degrees Celsius, DC 9-36 V with reverse polarity protection, measures 125 x 103 x 45 mm, mounts on a DIN rail or wall, and carries RS232/RS485 terminals, so where only one or two legacy gauges with serial ports remain, both can share a single unit. The latter measures 104 x 102 x 28 mm, mounts on a DIN rail or wall, is rated -20 to 70 degrees Celsius, and takes redundant power through both terminal block and DC jack, which is easier where cabinet space is tight.
How the two units get paired comes down to one number: how many access ports remain in the cabinet. Enough, and a single industrial wireless router finishes the job. Not enough, and the next step is to decide between adding ports and separating segments, then to fold addressing, rules, power and failure domain into the same calculation.
1. How many devices can a industrial wireless router handle?
Three numbers are not the same thing: physical access ports, wireless client capacity and concurrent sessions. Port count sets how many cables can be plugged in, wireless capacity sets how many terminals can associate, session count sets how many connections run at the same moment. USR-G809s offers two gigabit ports configurable as WAN or LAN, six LAN ports and two SFP fiber ports, one of which shares its slot with a copper port, with Wi-Fi 6 dual band rated at 256 clients. USR-G806w has three 10/100 Ethernet ports and supports up to 20 simultaneous wireless clients on the 2.4 GHz band. Beyond those numbers, a switch is hung below the egress unit to extend ports.
2. Signal bars are full, so why does throughput stay low?
Bars describe the quality of the radio link to the base station, not the throughput. Users on the same cell, antenna position and shielding by the cabinet all pull the real rate down. Published coverage figures usually come in two settings: around 200 m outdoors with nothing in the way, around 40 m indoors with partitions, and a shop floor dense with metal loses more again. The practical move is to lead the antenna outside the cabinet, then measure throughput and latency at the worst position, which beats watching bars.
3. The SIM is inserted but registration never completes. Which items come first?
Confirm first that the card is allowed in a router, since many plans restrict sharing with other devices. Then confirm the APN: IoT cards and VPDN private-network cards need the access point fixed when the card is issued, and an empty field looks exactly like absent local coverage, which is how it gets misdiagnosed on site. Finally check the priority order on dual-SIM models, and do not put the card in the wrong slot when the external card takes priority. If all three check out and it still fails, record signal strength and mounting position, move the antenna, then measure once more for comparison.
4. Will field data be lost during the minutes the link is down?
It depends on which side holds the buffer. Where data lands on the device and is replayed after the link recovers, changing platforms only changes where the data is received; where the buffering logic sits on the platform side, changing platforms means moving the replay logic as well. Asking that question at purchase beats fixing it afterwards. The test is to pull the primary link during commissioning, time the recovery, and confirm whether field operations were retrying or stalled during the wait.
5. Several VPN protocols exist. How is one chosen?
By what sits at the other end. Against a self-hosted server or one of the common open-source servers, enhanced OpenVPN is the easier route: a configuration imports in one click from an .ovpn file and a PKCS#12 certificate file, and one device can act as a client toward several servers or as a server itself. For links between devices where overhead matters, a lighter protocol suits better. USR-G816 supports PPTP, L2TP, IPSec, enhanced OpenVPN and GRE, which leaves more room at the far end.
6. Devices are spread over dozens of sites. How are parameters and firmware updated in bulk?
Through a remote management platform, not by logging into each unit. Parameters and firmware are pushed in bulk from the platform, the built-in web page can be opened remotely to change settings, and online state and signal quality are visible. Three alarm classes, offline, weak signal and traffic overrun, go out by email and SMS, with repeated push supported. Each gateway carries 50 M of VPN bandwidth for remote access, so channels to PLCs, HMIs or cameras are sized against that ceiling.
7. Only legacy gauges with serial ports remain. Is another box needed?
Check first whether the egress unit brings serial terminals. If it does, the gauge and the router share one device, saving a length of DIN rail, a power feed, a wiring run and an acceptance test. If it does not, a converter goes into the cabinet, and every added box is one more failure point and one more parameter sheet to back up. USR-G816 carries RS232/RS485 terminals at 1200 to 460800 bps, which removes one box at those points.
8. Shipping to the EU or North America: which certifications matter on a industrial wireless router?
List the mandatory items for the target market first, then match each one against the certificates model by model. Multiple PUSR devices have passed the EU EN 18031 cybersecurity standard, the cybersecurity requirement under the RED directive, and 3C, CE, FCC and RoHS are the other common ones. Certific